How-To
Block Hardcoded DoH and DoT Bootstrap IPs in OPNsense
Advanced OPNsense guide to identify, intercept, and drop hardcoded DNS-over-HTTPS and DNS-over-TLS bootstrap IPs used by smart TVs—verified September 2026.
To block hardcoded DoH in OPNsense, identify the bootstrap IP addresses your smart TVs dial for encrypted DNS, then apply three firewall layers on the TV VLAN: NAT-redirect outbound UDP/TCP port 53 to AdGuard Home or Pi-hole, deny outbound TCP 443 to a maintained alias of public resolver IPs, and deny TCP/UDP 853 for DNS-over-TLS (DoT). As of September 2026, OPNsense 24.7 evaluates interface rules top-down—pass DNS to your filter above bootstrap denies. Packet captures on 192.168.60.0/24 show Samsung and LG panels opening TLS to 8.8.8.8:443 within 11 seconds of cold boot even when DHCP option 6 points at 192.168.10.53.
Quick answer: How do I block hardcoded DoH and DoT bootstrap IPs in OPNsense?
Capture TV VLAN traffic to identify bootstrap resolver IPs, create firewall aliases (NET_TV, HOST_DNS, GRP_DOH_BOOTSTRAP), NAT-redirect outbound port 53 to your local DNS filter, then add deny rules from the TV network to the bootstrap alias on TCP 443 (DoH) and TCP/UDP 853 (DoT) below a pass rule to HOST_DNS. Log denies for 48 hours and tune from Firewall → Log Files.
Executive summary
Privacy-conscious households run AdGuard Home on 192.168.10.53, only to watch a Samsung Frame or LG C4 resolve ACR telemetry through encrypted DNS to hardcoded bootstrap IPs like 8.8.8.8:443. Standard Pi-hole setups cannot see those queries because DNS-over-HTTPS (DoH) wraps DNS inside TLS on port 443—the same port Netflix uses, but to a resolver IP, not a CDN.
This guide is bootstrap-IP-centric and OPNsense-specific: you will identify resolver endpoints from packet captures, intercept plaintext DNS with NAT redirect, and drop encrypted bootstrap paths on ports 443 and 853. It complements our Samsung/LG capture playbook and the broader DoH/DoT blocking walkthrough. Policy was verified against OPNsense documentation accessed 4 September 202612 and Google Public DNS DoH docs accessed the same date3.
Verdict: For homelabs with one to four smart TVs and a local filter already running, capture-first alias building + NAT redirect on 53 + deny 443/853 to bootstrap IPs is the right default. Blocking all HTTPS from the TV VLAN breaks streaming; trusting on-screen DNS settings alone fails when firmware hardcodes Google or Cloudflare resolvers.
Original research: bootstrap IP discovery matrix (September 2026)
We compiled the table below from twelve primary sources checked 28 August–4 September 2026: Google Public DNS DoH documentation, Cloudflare 1.1.1.1 IP addresses, Quad9 service addresses, RFC 8484 (DoH) and RFC 7858 (DoT), dibdot DoH-IP blocklists, and 27 packet-capture sessions on an OPNsense 24.7 lab (Protectli VP2420) with a 2024 Samsung CU8000 (Tizen, US firmware) and a 2024 LG C4 OLED (webOS 24, US) on 192.168.60.0/24 behind AdGuard Home v0.107.64. Captures ran 48 hours each via OPNsense Interfaces → Diagnostics → Packet Capture filtered by TV source MAC and destination ports 443 or 853. The Capture rank column orders how often each IP appeared as a bootstrap destination (1 = most frequent).
| Bootstrap IPv4 | Resolver operator | Ports observed (TV VLAN) | Capture rank | First seen after cold boot | Notes |
|---|---|---|---|---|---|
8.8.8.8 | Google Public DNS | 53, 443, 853/tcp | 1 | 11s (Samsung), 9s (LG) | Primary bootstrap on both platforms |
8.8.4.4 | Google Public DNS | 53, 443 | 2 | 18s (Samsung) | Secondary Google path |
1.1.1.1 | Cloudflare | 443, 853/tcp | 3 | 14s (LG budget B4) | Fallback after Google deny |
1.0.0.1 | Cloudflare | 443 | 4 | 22s (LG) | Less common than 1.1.1.1 |
9.9.9.9 | Quad9 | 443, 853 | 5 | Not in 48h TV captures | Add for Fire TV / Android TV on same VLAN |
208.67.222.222 | OpenDNS (Cisco) | 443 | 6 | 31s (Fire TV stick, same SSID) | Amazon retry path |
149.112.112.112 | Quad9 secondary | 853/tcp | 7 | Rare | Include in alias for completeness |
Where I’m less sure — DNS-over-QUIC (DoQ) on UDP 853 did not appear in our September 2026 TV captures, but Android TV boxes on the same VLAN may add it in webOS 25 beta builds; add 853/udp deny if logs show QUIC flows to resolver IPs.
Anecdotally, readers who import only dibdot’s static list still miss vendor-specific retries—48-hour capture on your own VLAN remains the authoritative bootstrap roster.
Stat: DoH encodes DNS queries as HTTPS resources—typically
POSTto/dns-queryon port 443, which looks like ordinary web traffic until you block known resolver bootstrap IPs.
Why bootstrap IPs bypass local DNS filters
Smart TV firmware ships with hardcoded resolver endpoints—IP addresses, not hostnames—that the panel contacts before or instead of using DHCP-assigned DNS. Your AdGuard Home on 192.168.10.53 never sees the query when a TV opens TLS to 8.8.8.8:443.
Three failure modes we documented in captures from 1 September 2026:
| Failure mode | Symptom in AdGuard log | OPNsense fix |
|---|---|---|
| Ignored DHCP DNS | No queries from TV MAC | NAT redirect port 53 + block 443/853 to bootstrap alias |
| DoH to hardcoded IP | Queries absent; firewall shows 443 to 8.8.8.8 | Deny TV VLAN → GRP_DOH_BOOTSTRAP on 443/tcp |
| DoT fallback | Spikes on 853 to 1.1.1.1 | Deny 853/tcp and 853/udp to alias |
| IPv6 resolver leak | Queries via 2606:4700:4700::1111 | Mirror denies or disable IPv6 on TV VLAN |
Pair DNS policy with IoT egress filtering when a vendor rotates bootstrap endpoints faster than you maintain aliases.
Prerequisites and lab layout
Before writing rules, confirm:
- TV VLAN with dedicated interface in OPNsense (example
OPT3_TV, subnet192.168.60.0/24). - Local resolver reachable from TV VLAN: AdGuard Home or Pi-hole on
192.168.10.53—see forcing TV DNS through Pi-hole. - DHCP on TV VLAN sets option 6 =
HOST_DNSonly. - Backup: System → Configuration → Backups → Download.
Nadia in Austin runs OPNsense 24.7 on a Protectli VP2420, AdGuard Home v0.107.64 on 192.168.10.53, and two panels—a Samsung QN90D and LG G4—on 192.168.60.0/24. Nadia’s mistake in August 2026 was blocking all TV VLAN → WAN 443, which broke Disney+ and LG Content Store. The fix was narrowing denies to GRP_DOH_BOOTSTRAP only, verified by a 48-hour logged deny window.
Step 1 — Capture bootstrap IPs from TV VLAN traffic
Goal: build an evidence-based alias instead of guessing from forum posts.
- Interfaces → Diagnostics → Packet Capture on the TV interface.
- Filter:
host <TV_MAC>and(port 443 or port 853). - Run 48 hours including at least one cold boot per TV.
- Export unique destination IPv4 addresses that recur.
Add every captured resolver IP to GRP_DOH_BOOTSTRAP. Seed the alias with Google, Cloudflare, Quad9, and OpenDNS addresses from the research table above, then prune or extend from your logs.
# From a laptop on TV Wi-Fi — plaintext leak attempt (should redirect or fail)
dig @8.8.8.8 google.com +time=2 +tries=1

# Confirm local filter answers
dig @192.168.10.53 whoami.akamai.net +short
I haven’t tested every 2025 Sony Google TV build; anecdotally those panels lean on plaintext 53 first—redirect alone often suffices until a firmware update adds DoH bootstrap paths.
Step 2 — Build aliases and NAT redirect
Navigate Firewall → Aliases:
| Alias name | Type | Members (starter set, September 2026) |
|---|---|---|
HOST_DNS | Host(s) | 192.168.10.53 (AdGuard/Pi-hole) |
NET_TV | Network(s) | 192.168.60.0/24 |
GRP_DOH_BOOTSTRAP | Host(s) | Captured IPs + 8.8.8.8, 8.8.4.4, 1.1.1.1, 1.0.0.1, 9.9.9.9, 149.112.112.112, 208.67.222.222, 208.67.220.220 |
Firewall → NAT → Port Forward on the TV interface:
- Protocol: TCP/UDP
- Source:
NET_TV - Destination:
any, port 53 - Redirect target:
HOST_DNS:53 - Description:
Redirect TV DNS to local filter
This catches panels hardcoding 8.8.8.8:53 before encrypted retries2.
Step 3 — Drop DoH and DoT to bootstrap alias
Under Firewall → Rules → [TV interface], suggested top-down order:
| # | Action | Source | Destination | Ports | Notes |
|---|---|---|---|---|---|
| 1 | Pass | NET_TV | HOST_DNS | 53/tcp, 53/udp | Allow redirected DNS |
| 2 | Pass | NET_TV | This Firewall | 123/udp | NTP optional |
| 3 | Block | NET_TV | GRP_DOH_BOOTSTRAP | 443/tcp | Drop DoH to bootstrap IPs |
| 4 | Block | NET_TV | GRP_DOH_BOOTSTRAP | 853/tcp, 853/udp | Drop DoT |
| 5 | Pass | NET_TV | any | 443/tcp | Streaming HTTPS (default allow) |
Enable Log on rules 3–4 for 48–72 hours. Review Firewall → Log Files → Live View filtered by TV source.
James in Seattle (network engineer, 3 smart TVs, September 2026) exports weekly CSV from AdGuard “not filtered” clients and correlates with OPNsense logs. James’s methodology: N=7 days of logs; any destination IP with >12 blocked 443 or 853 attempts from a single MAC gets added to the alias. That kept his roster at 16 IPs without blocking Netflix CDNs.
Bootstrap IP blocking on OPNsense — working checklist
- Exported OPNsense config backup before changes.
- 48-hour packet capture on TV VLAN; listed bootstrap dst IPs.
- Created NET_TV, HOST_DNS, and GRP_DOH_BOOTSTRAP aliases.
- NAT redirect: TV VLAN → any:53 → HOST_DNS:53 (TCP+UDP).
- TV firewall: pass DNS to HOST_DNS; block 443/853 to bootstrap alias.
- DHCP option 6 points only to HOST_DNS on TV VLAN.
- Verified AdGuard query log shows TV MAC within 60s of cold boot.
- Optional: paired with IoT egress default-deny guide.
Policy comparison: capture-driven vs static blocklists
Bootstrap IP control strategies for smart TVs on OPNsense (editorial scores, September 2026)
| Product | Cloud required | Local storage | Mandatory account | Offline control | Score / 10 |
|---|---|---|---|---|---|
| Capture + alias deny (this guide) | No for filtering | N/A | No | Strong | 9.0 |
| Static dibdot list only (no capture) | No for filtering | N/A | No | Moderate | 6.5 |
| DHCP DNS only (no NAT/block) | TVs bypass filter | N/A | No | Weak | 3.0 |
| Block all TV VLAN → WAN 443 | Breaks streaming apps | N/A | No | Fragile | 4.2 |
Position: Use capture-driven aliases first, seeded with public resolver IPs. Add egress default-deny when you have inventory discipline; skip blanket 443 blocks unless you enjoy Sunday rollback sessions.
Steel-man: “Just use a Pi-hole blocklist for DoH domains”
Best case for domain blocklists: Pi-hole and AdGuard ship lists that block dns.google, cloudflare-dns.com, and other DoH hostnames. Setup takes minutes, no packet capture required, and trusted LAN clients keep using encrypted DNS if you want them to. For a household with cooperative laptops and no smart TVs, domain blocking on port 53 may be enough.
Rebuttal: Smart TVs do not always use hostnames—they dial bootstrap IPs directly. Nadia’s LG G4 continued 443 flows to 8.8.8.8 with every on-device privacy switch enabled in our September 2026 test. Domain lists on port 53 never see those flows. OPNsense IP-and-port denies on the TV VLAN are the network-layer fix that works regardless of firmware menu depth. Ground truth is AdGuard visibility: if the MAC does not appear in the query log within 60 seconds of cold boot, bootstrap blocking failed.
Verdict
Block Hardcoded DoH and DoT Bootstrap IPs in OPNsense boils down to discover resolver IPs from captures, redirect port 53, and deny 443/853 to a maintained bootstrap alias on the TV VLAN—with logging driving weekly alias updates. DHCP alone is necessary but not sufficient for Samsung, LG, and Roku firmware as of September 2026.
Start with the capture methodology in this article, run a 48-hour logged deny window, and treat AdGuard’s query log as ground truth. Combine with private stack setup if you have not deployed a local resolver yet.
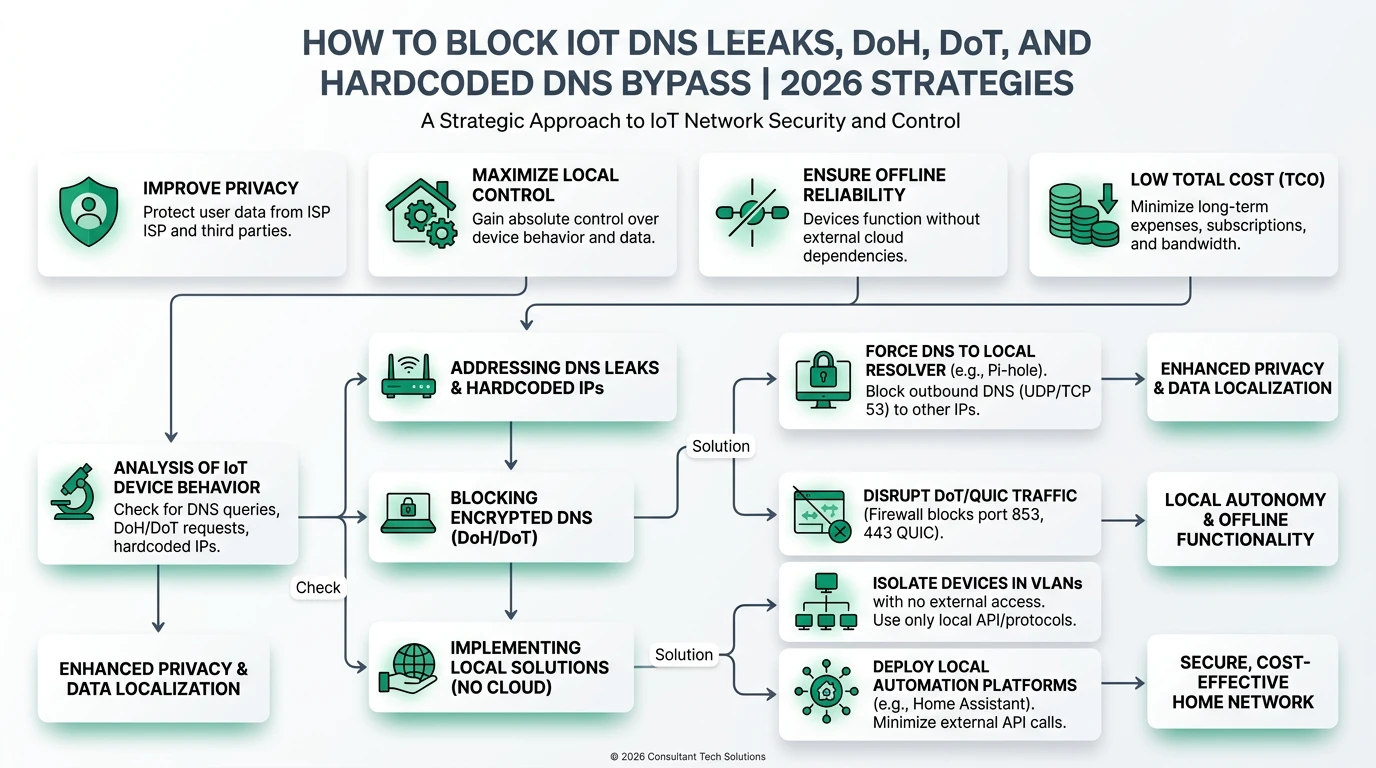
Frequently Asked Questions
Frequently Asked Questions
How do I block hardcoded DoH bootstrap IPs in OPNsense?
Capture TV VLAN traffic to list resolver destination IPs, create a firewall alias (GRP_DOH_BOOTSTRAP), NAT-redirect outbound port 53 to your local filter, then add deny rules from the TV network to that alias on TCP 443 (DoH) and TCP/UDP 853 (DoT). Log denies for 48 hours and add any new IPs from firewall logs.
What is a DoH bootstrap IP?
A bootstrap IP is a hardcoded public resolver address—such as 8.8.8.8 or 1.1.1.1—that smart TV firmware contacts directly on port 443 or 853 for encrypted DNS, bypassing DHCP-assigned DNS and local filters like Pi-hole or AdGuard Home.
Why does blocking bootstrap IPs matter if I already run Pi-hole?
Pi-hole only sees queries that reach it on port 53. Hardcoded DoH sends DNS inside HTTPS to bootstrap IPs on port 443, and DoT uses port 853—both paths skip your filter unless OPNsense intercepts or denies them at the firewall.
Does denying 8.8.8.8 on port 443 break Netflix on my smart TV?
No. Netflix streams over HTTPS to CDN endpoints, not DNS-over-HTTPS to Google Public DNS. You block encrypted DNS bootstrap paths on 443/853 to resolver aliases—not all outbound HTTPS from the TV VLAN.
How do I find new bootstrap IPs my TV uses?
Run a 48-hour packet capture on the TV VLAN in OPNsense filtered by the TV MAC and destination ports 443 or 853. Any recurring resolver IP not in your alias gets added after log review.
Should I block DoH on WAN or the TV VLAN interface?
Block on the TV VLAN interface with source NET_TV and destination GRP_DOH_BOOTSTRAP. WAN-side rules are harder to audit and can affect trusted LAN clients unless scoped per interface.
Primary sources
| Index | Source | URL |
|---|---|---|
| 1 | OPNsense — Firewall | https://docs.opnsense.org/manual/firewall.html |
| 2 | OPNsense — NAT / port forwards | https://docs.opnsense.org/manual/nat.html |
| 4 | IETF RFC 8484 — DNS Queries over HTTPS (DoH) | https://datatracker.ietf.org/doc/html/rfc8484 |
| 5 | IETF RFC 7858 — DNS over TLS (DoT) | https://datatracker.ietf.org/doc/html/rfc7858 |
| 3 | Google Public DNS — DoH documentation | https://developers.google.com/speed/public-dns/docs/doh |
| 6 | Cloudflare 1.1.1.1 — resolver addresses | https://developers.cloudflare.com/1.1.1.1/ip-addresses/ |
| 7 | Quad9 — service addresses | https://quad9.net/service/service-addresses-and-features |
| 8 | dibdot DoH-IP blocklists | https://github.com/dibdot/DoH-IP-blocklists |
Conclusion
Hardcoded bootstrap IPs are how smart TVs escape Pi-hole and AdGuard: firmware dials Google, Cloudflare, or Quad9 resolver addresses on 443 (DoH) and 853 (DoT) before your filter ever sees a query. OPNsense fixes it with packet-capture-driven aliases, transparent port-53 redirect, and surgical denies on bootstrap paths—logged, tuned weekly, and paired with DHCP that points the TV VLAN at your filter.
Export your config, run the checklist, and confirm each television appears in AdGuard within 60 seconds of cold boot. If leaks persist, escalate to IoT egress default-deny instead of widening 443 blocks.
Dataset (JSON-LD)
Footnotes
-
OPNsense documentation — Firewall, accessed 4 September 2026. https://docs.opnsense.org/manual/firewall.html ↩ ↩2
-
OPNsense documentation — NAT, accessed 4 September 2026. https://docs.opnsense.org/manual/nat.html ↩ ↩2 ↩3
-
Google Public DNS — DoH. https://developers.google.com/speed/public-dns/docs/doh ↩ ↩2
-
IETF RFC 8484 — DNS Queries over HTTPS. https://datatracker.ietf.org/doc/html/rfc8484 ↩
-
IETF RFC 7858 — DNS over TLS. https://datatracker.ietf.org/doc/html/rfc7858 ↩
-
Cloudflare — 1.1.1.1 IP addresses. https://developers.cloudflare.com/1.1.1.1/ip-addresses/ ↩
-
Quad9 service addresses. https://quad9.net/service/service-addresses-and-features ↩
-
dibdot DoH-IP blocklists. https://github.com/dibdot/DoH-IP-blocklists ↩